Microsoft Outage Triggers Phishing Warnings as Hackers Target Users with Fake Deletion Emails
Microsoft has warned users about a new phishing campaign exploiting a recent service outage to steal passwords and login credentials via malicious links.

- Microsoft warned users about a phishing campaign exploiting the recent service outage.
- Hackers are sending fake emails claiming delayed messages will be deleted within 24 hours.
- Fraudulent emails attempt to steal login credentials and passwords via malicious links.
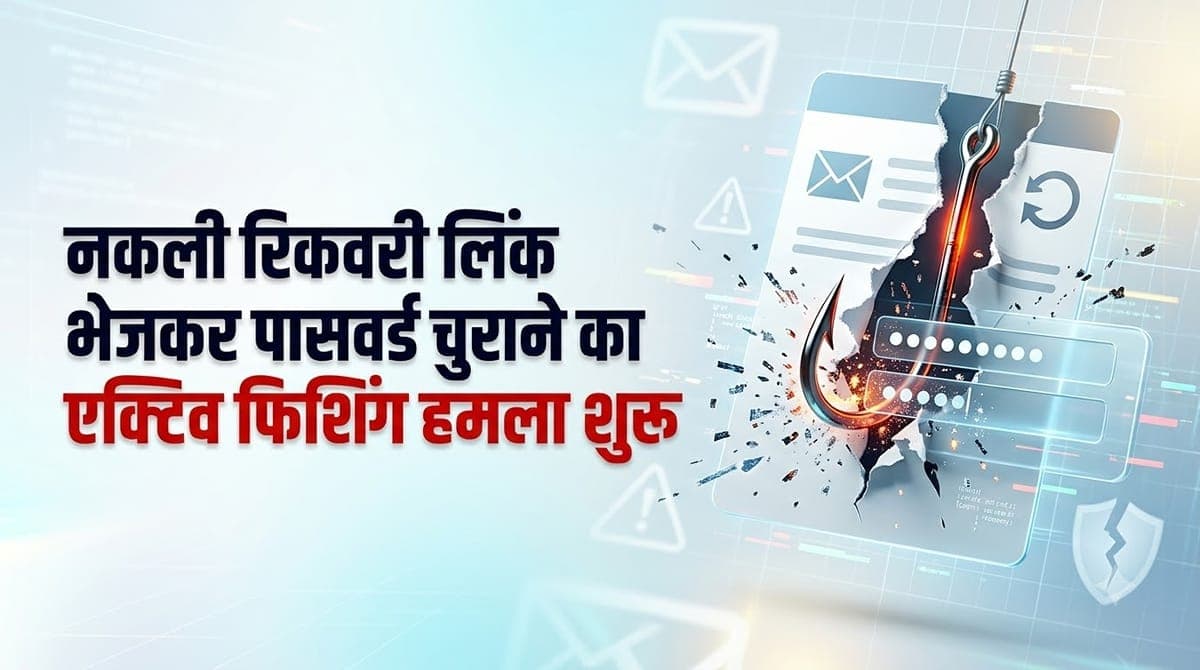
Microsoft has alerted its user base regarding an active cyber threat exploiting the aftermath of a recent system disruption. The technology giant reported that malicious actors are attempting to capitalize on the technical difficulties by launching targeted phishing campaigns designed to capture sensitive login credentials and passwords.
Recent Outage Disruptions
The security warning follows a significant disruption that affected multiple Microsoft platforms, leaving critical applications unavailable for a prolonged duration. During this service failure, consumers experienced difficulties accessing collaboration tools, email clients, and various office productivity software necessary for their daily routines.
Phishing Campaign Tactics
According to threat intelligence findings shared on social media, cybercriminals are impersonating official service notifications to deceive unsuspecting individuals. These fraudulent messages mimic legitimate corporate alerts in an effort to lower user defenses and prompt immediate action without proper verification.
False Deletion Threats
The fraudulent emails specifically warn recipients that messages held back during the technical failure are at risk of permanent deletion within a specific timeframe. The attackers claim that unread or delayed communications will vanish unless the recipient follows an embedded web link immediately.
Targeted Information Theft
By manufacturing a sense of urgency regarding the 24-hour expiration claim, the perpetrators aim to trick users into bypassing standard safety checks. Security analysis indicates that successfully compromising these accounts could expose sensitive personal details, including banking information and access to connected devices like smartphones and laptops.
Identified Malicious Domains
The corporate threat monitoring division has successfully tracked and identified several specific domains associated with this malicious email distribution effort. The flagged sender domains include addresses such as moments-notice, planetmaison, and newbooker, which are being used to relay the fraudulent correspondence.
Official Security Guidance
In response to these fraudulent activities, the software provider has strongly advised customers to exercise extreme caution when handling unsolicited electronic mail. Users have been explicitly instructed to refrain from interacting with unfamiliar links or downloading attachments from unverified sources claiming to resolve outage-related communication backlogs.
Restoration of Services
While technical teams worked to restore normal operations across the affected platforms after a multi-hour interruption, the subsequent wave of fraudulent outreach highlights lingering secondary risks following major digital incidents. Consumers remain the primary target for opportunistic fraudsters attempting to leverage system instability for unauthorized access.
- Cybercriminals are exploiting the recent Microsoft service disruption to launch phishing attacks.
- Fake emails threaten that unread messages will be deleted within 24 hours to create panic.
- Microsoft threat intelligence identified specific fraudulent domains used in the campaign.
- Users are urged to avoid clicking on suspicious links contained in unexpected notifications.
Spotted an error? · Our editorial policy
UP NEXTDadasaheb Phalke International Film Festival Awards 2026: Taylor Swift and James Cameron Among WinnersOther angles · #cybersecurity
Timeline →- NewsFBI Chief Warns Cybercriminals as US Financial Sector Faces Vendor Data Breach and Leadership Shakeup
- NewsHyderabad-Based GenvenX Technologies Outlines Expansion Across AI, Cybersecurity, and FinTech
- NewsEnterprise Cybersecurity Shifts Focus Toward Cyber Resilience Amid AI-Driven Threats
- NewsRussia-Linked Hacking Group Claims Cyberattack on Third-Party Vendor Affecting JPMorgan Chase, Visa, and Mastercard
More from Technology
Anthropic Researcher Claims AI-Assisted Proof for the Riemann Hypothesis
Grand Theft Auto VI Becomes Largest Entertainment Launch in History
Trump Backs Jensen Huang’s Return to Nvidia Amid Board Resistance and Intelligence Scrutiny