Russia-Linked Hacking Group Claims Cyberattack on Third-Party Vendor Affecting JPMorgan Chase, Visa, and Mastercard
A Russia-linked hacking group claimed responsibility for a cyberattack on a third-party service provider, potentially exposing limited customer data from JPMorgan Chase, Visa, and Mastercard.

- A Russia-linked hacking group named n0n claimed responsibility for a cyberattack on a third-party subcontractor.
- JPMorgan Chase stated attackers may have accessed vendor marketing data like customer names and email addresses, but banking systems were unaffected.
- Visa and Mastercard confirmed third-party vendor incidents occurred, but verified that payment processing and card numbers were not compromised.
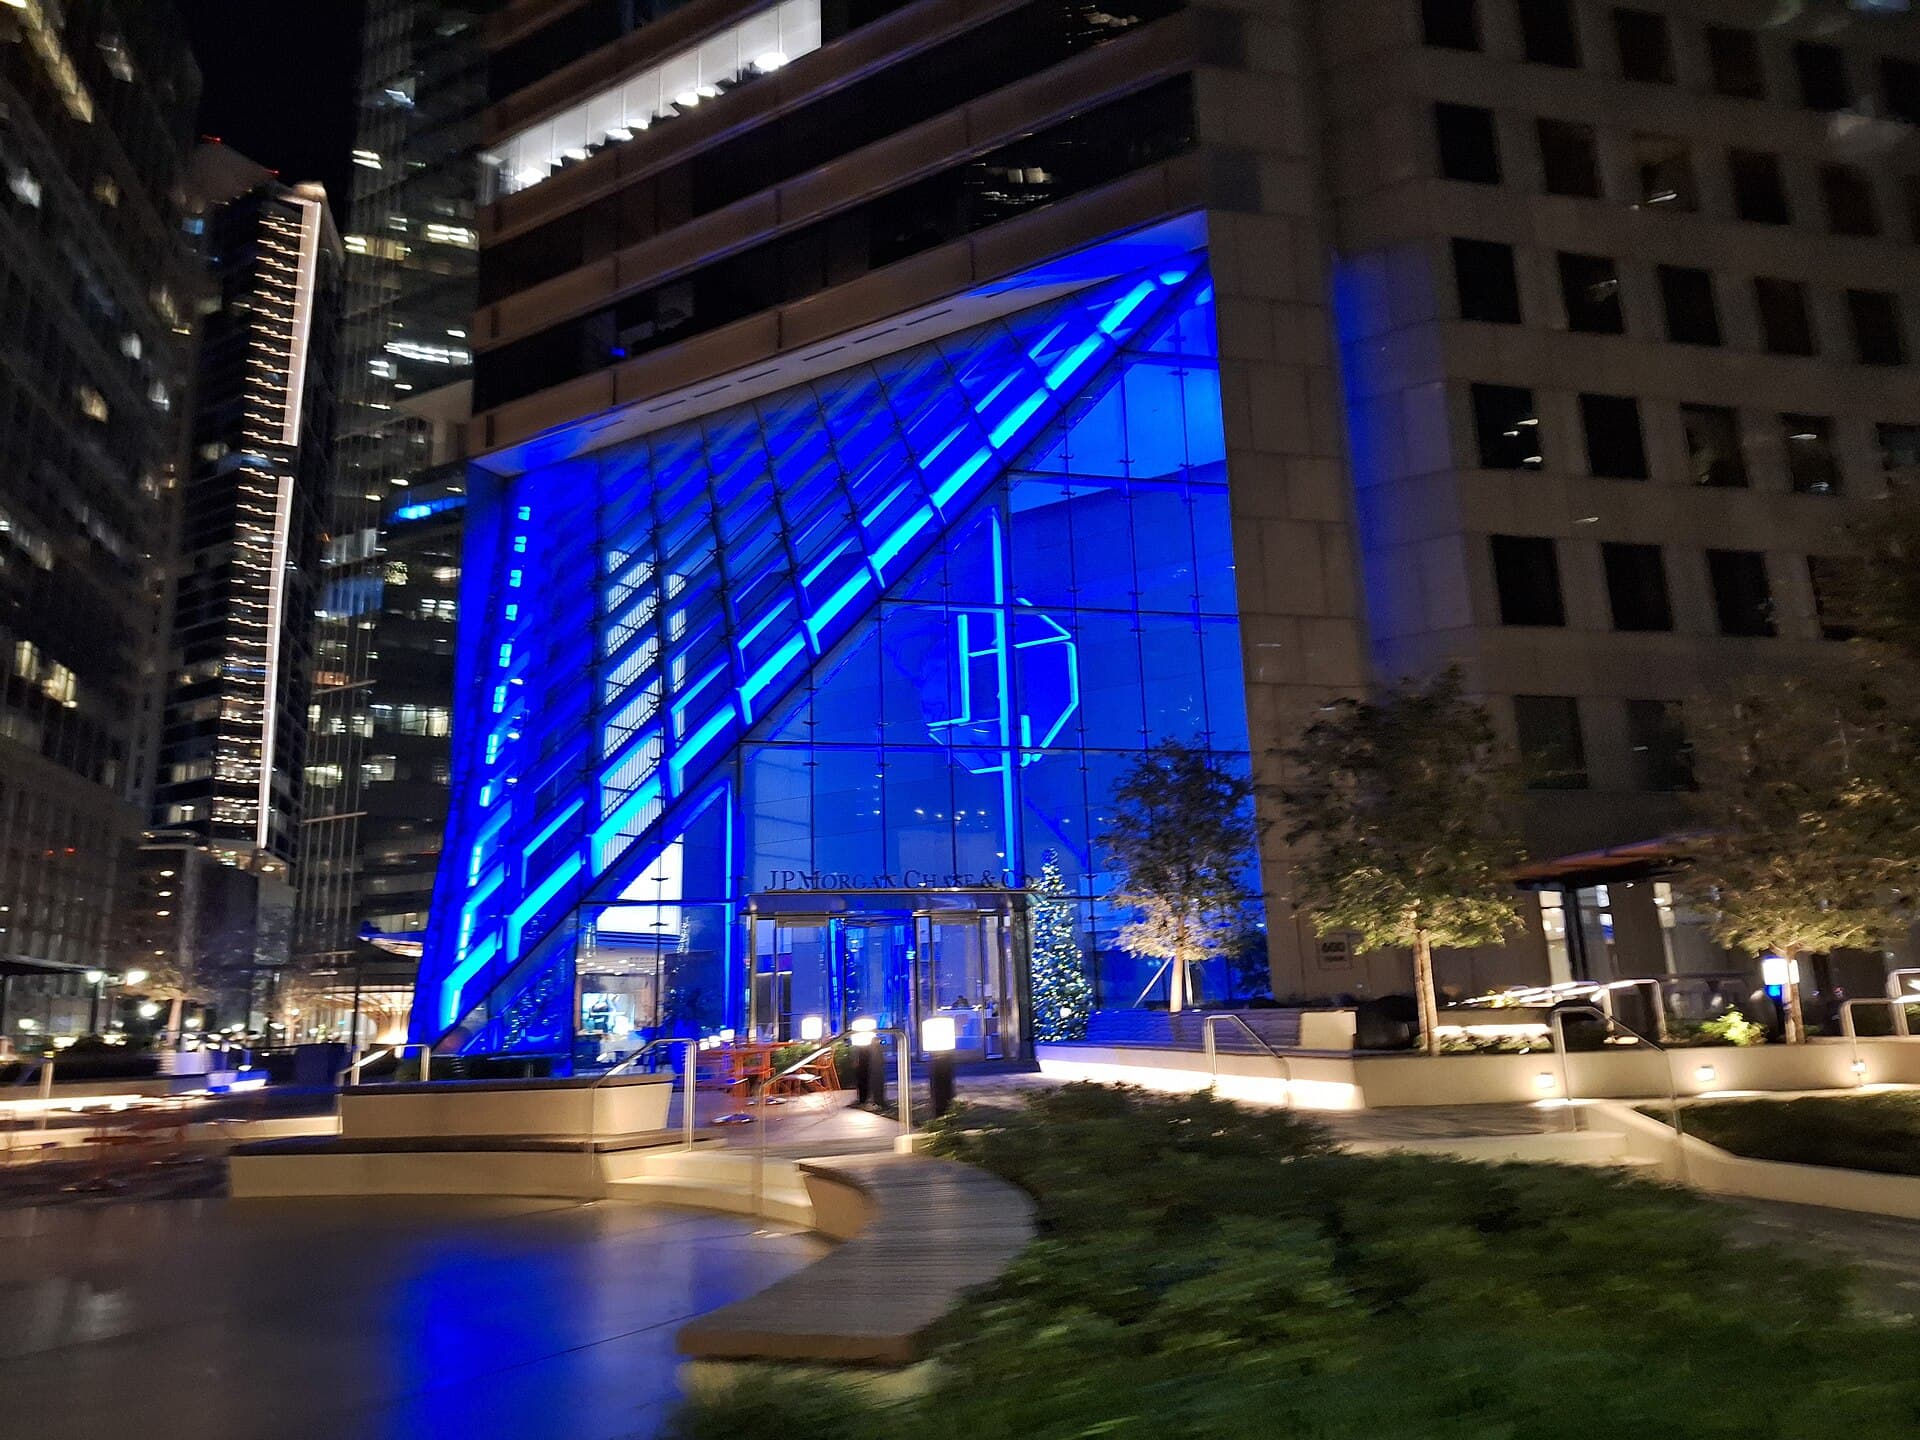
A Russia-linked hacking outfit named n0n claimed responsibility for a cyberattack targeting a third-party service provider linked to major financial institutions, raising concerns over customer data exposure. The incident was acknowledged by JPMorgan Chase, Visa, and Mastercard on November 19, following the release of documents by the hacking group purporting to show evidence of the breach. Cybersecurity firm SOCRadar stated it was informed of the claims but could not independently verify the authenticity of the published documents. According to SOCRadar, the n0n group emerged in September and has claimed responsibility for attacks on nearly 200 companies globally.
Responses From Financial Institutions
JPMorgan Chase stated via social media platform X that its preliminary investigation indicated attackers accessed marketing information held by vendors, potentially including customer names and email addresses. The bank maintained that its core banking systems remained unaffected, services continued without disruption, and the incident was entirely unrelated to recent technical system outages experienced alongside United Airlines and the US National Security Agency.
Visa confirmed that an Asia-Pacific-based service provider was targeted, but stressed that its own systems and payment processing infrastructure—including customer card numbers—were untouched by the breach. Similarly, Mastercard reported that the incident involved a service provider and that affected data was restricted to non-payment information tied to a specific cardholder benefits programme. Mastercard noted that its teams are collaborating with the vendor to evaluate the situation and assist impacted cardholders.
Ongoing Investigation and Risks
While all three corporations ruled out any compromise of financial and payment data, the episode underlines the vulnerability of relying on third-party subcontractors to handle customer records. Investigations remain ongoing, with final details regarding the exact volume of affected users and fully accessed data yet to be officially disclosed.
- The n0n hacking group published documents claiming a breach of financial vendors on November 19.
- JPMorgan Chase, Visa, and Mastercard confirmed subcontractor incidents but assured the public that core financial and payment data remained safe.
- Cybersecurity analysts stated the authenticity of the leaked documents could not be independently verified.
Spotted an error? · Our editorial policy
UP NEXTSanjay Kapoor Stars in ‘Unexpected – Safed Sach’ Based on 2024 Dehradun CaseOther angles · #cybersecurity
Timeline →- NewsFBI Chief Warns Cybercriminals as US Financial Sector Faces Vendor Data Breach and Leadership Shakeup
- NewsHyderabad-Based GenvenX Technologies Outlines Expansion Across AI, Cybersecurity, and FinTech
- NewsEnterprise Cybersecurity Shifts Focus Toward Cyber Resilience Amid AI-Driven Threats
- NewsWhite House Names Kirsten Davies as National Cyber Director Following Critical Infrastructure Outages
More from Technology
Anthropic Researcher Claims AI-Assisted Proof for the Riemann Hypothesis
Grand Theft Auto VI Becomes Largest Entertainment Launch in History
Trump Backs Jensen Huang’s Return to Nvidia Amid Board Resistance and Intelligence Scrutiny